
See how fast your threats would be caught and contained. Start with a free assessment.
Key Points
- Continuous monitoring across endpoint, identity, network, and cloud.
- Proactive threat hunting, not just waiting for alarms.
- Active containment in minutes, at any hour.
- Full incident response when an attack does occur.
Threat detection and response is the continuous work of watching your environment, spotting attacks, and stopping them. However, those attacks do not keep business hours. They can appear on nights, weekends, and holidays, precisely when most teams are offline. IS&T provides genuine 24/7 detection and response: always-on monitoring across your organization’s entire environment, proactive hunting for threats already inside, and active containment that stops confirmed attacks in minutes, whenever they happen.
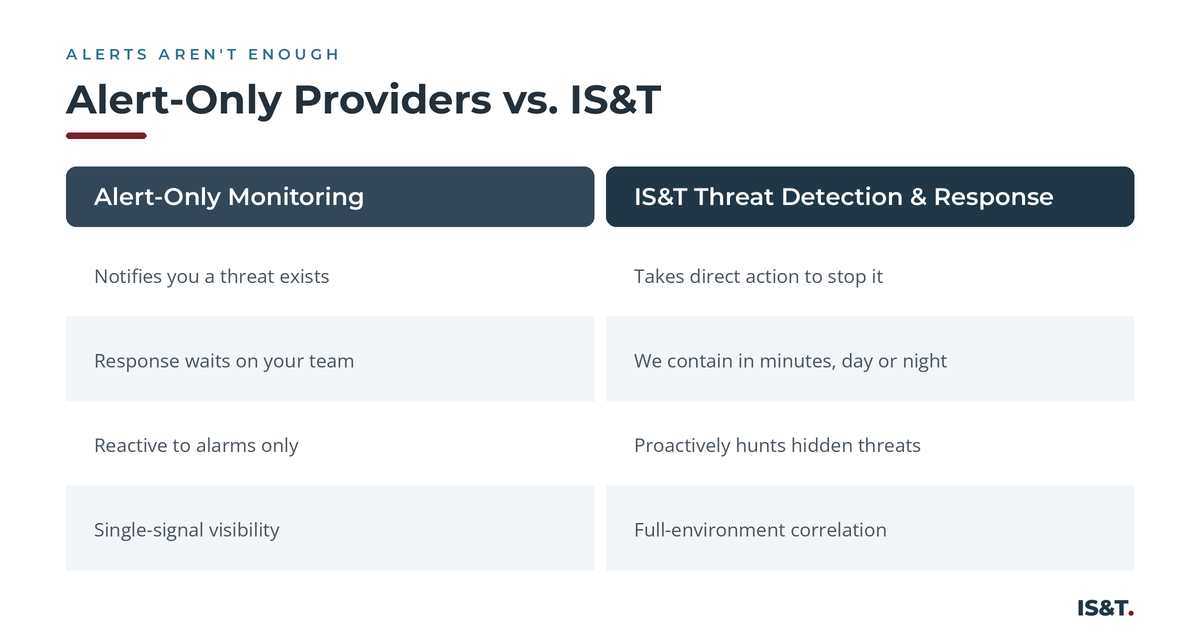
Alerts are not protection
Being told about a fire is not the same as putting it out. Plenty of services will notify you that something looks wrong but wait for you to act. If that notification lands at 2 a.m. on a Saturday, the attacker has hours before anyone reads it. Real protection means someone is watching and empowered to respond, right then.
From suspicious signal to contained threat
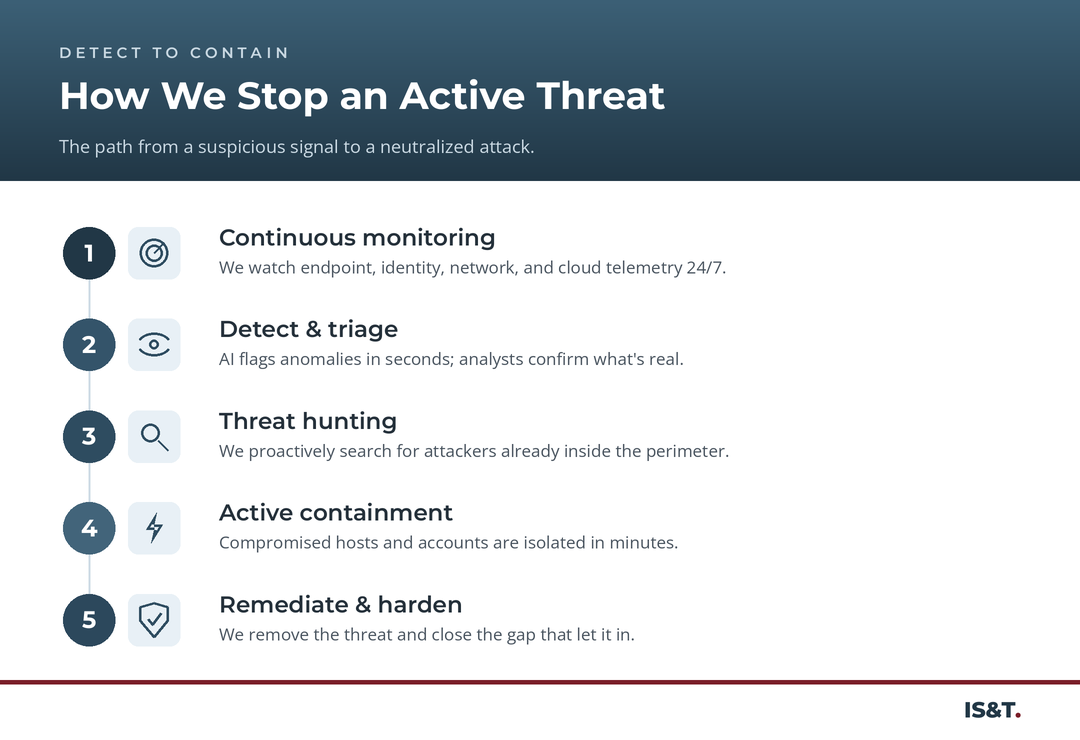
IS&T’s response follows a clear, fast path. We monitor continuously, detect and triage anomalies in seconds, hunt proactively for hidden threats, contain confirmed attacks by isolating systems and accounts, and then remediate and harden so the same gap cannot be used twice.
Proactive threat hunting
The most dangerous attackers are the ones sitting quietly inside a network, having slipped past the alarms. IS&T goes looking for them, using threat intelligence and hunting techniques mapped to the MITRE ATT&CK framework to find and evict threats before they act, rather than waiting for them to make a move.
Incident response when it counts
If an incident does occur, your business is not left on its own. Our team steps in to contain the damage, investigate what happened, get your organization back to normal operations quickly, and then applies the lessons so your defenses are stronger than before.
Do not wait for the 2 a.m. alert no one is watching. Get 24/7 detection and response protecting your business now.
Frequently Asked Questions
What is 24/7 threat detection and response?
It is a service that continuously monitors your organization’s environment for threats, investigates them the moment they appear, and takes action to stop them, at any hour. It combines automated detection with human analysts and active containment.Why does 24/7 coverage matter?
Attackers deliberately strike nights, weekends, and holidays when defenders are offline. A threat detected at 3 a.m. and left until morning has hours to spread. Around-the-clock detection and response removes that window.What does active containment mean?
Rather than only alerting you, our analysts take direct action to stop a confirmed threat: isolating a compromised device, disabling an account, or blocking malicious traffic, in minutes, so the attack cannot progress.Is threat hunting included?
Yes. Beyond responding to alerts, IS&T proactively hunts for attackers who may already be inside but have not tripped an alarm, using threat intelligence and techniques mapped to the MITRE ATT&CK framework.