
See how a managed SOC would fit your environment. Book a short walkthrough with our team.
Key Points
- SOC-as-a-Service gives you a full security operations center as a predictable monthly subscription.
- Choose co-managed, which wraps your existing tools, or fully managed by our team.
- Our analysts detect in seconds and contain confirmed threats in under 15 minutes.
- No hiring, training, or 24/7 shift scheduling for a security team.
A security operations center, or SOC, is the team and technology that watches your business environment for threats and responds when one appears. Building one in-house means hiring hard-to-find analysts, buying enterprise tooling, and covering three shifts all day, every day. SOC-as-a-Service gives your business all of that as a subscription. IS&T's managed SOC monitors your business 24/7, investigates every real signal, and takes direct action to contain threats. All of this is available for a fraction of the cost of equipping a team yourself.
What a managed SOC does for you
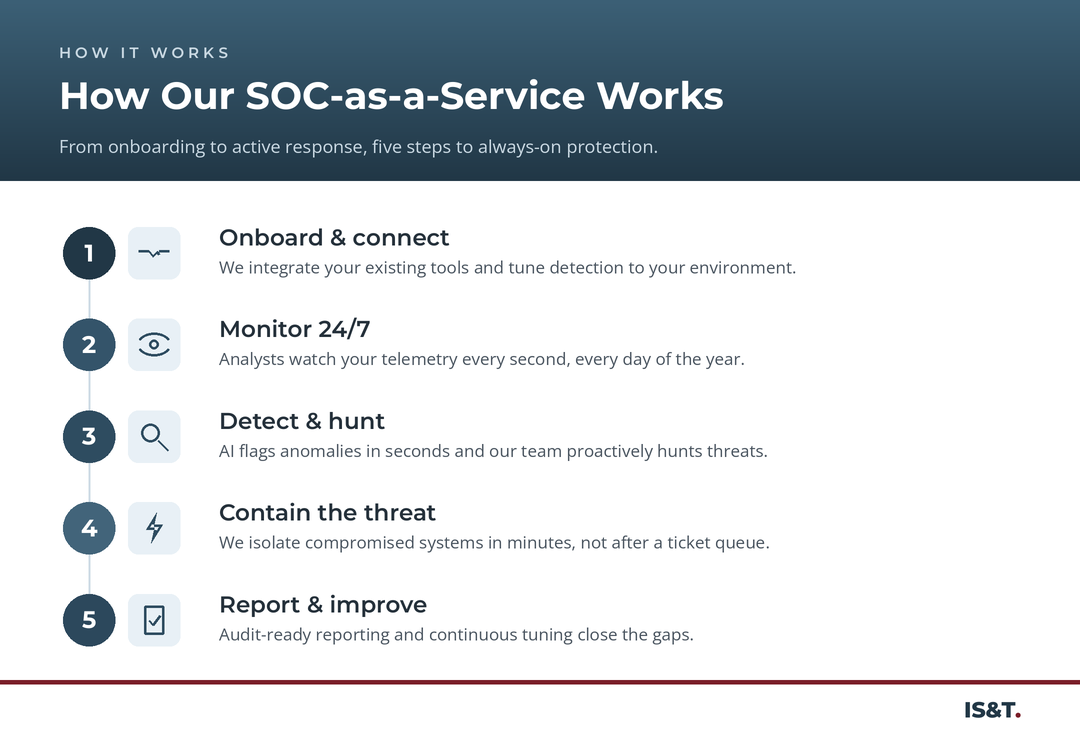
Your tools already generate alerts. The difficulty is that a staff member has to watch them at all hours of the day and night, differentiate the real threats from the noise, and act fast when it matters. That is what a managed SOC provides: trained analysts, backed by AI-driven detection, managing the supervising and the responding so your team does not have to.
Co-managed or fully managed, your choice
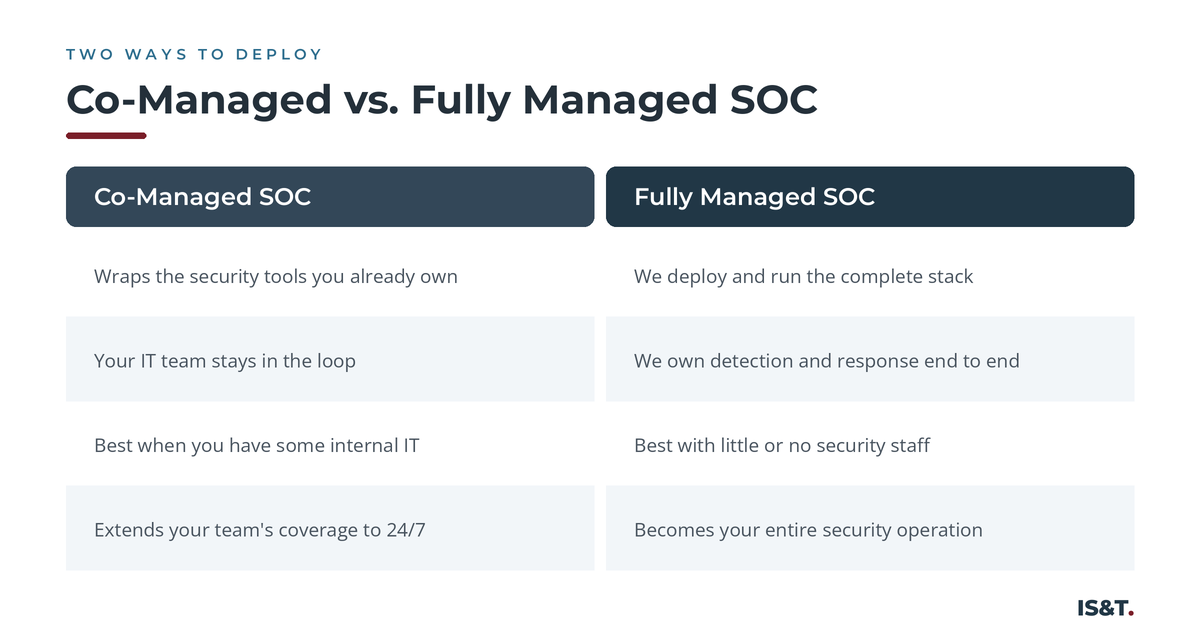
Not every business requires the same model. If your business has an internal IT team and existing security tools, a co-managed SOC extends those resources to 24/7 coverage without stripping anything away. If your business has little to no in-house security staff, a fully managed SOC is capable of becoming your entire security operation.
We take action, not just note it
Many providers stop at sending you an alert. Ours does not. When we confirm a threat, we contain it, isolate the affected device, disable the compromised account, and cut off the attacker's path, all within minutes. The difference between an alert and an action is often the difference between a non-event and a breach.
Predictable cost, enterprise capability
Hiring even one skilled SOC analyst is expensive, and for comprehensive protection your business could need several to cover operations 24/7. SOC-as-a-Service turns that unpredictable staffing challenge into a flat monthly cost, while giving your business tools and threat intelligence that would be out of reach for most mid-sized businesses on their own.
Ready to see what always-on protection looks like for your business? Book a walkthrough and we will map a managed SOC to your environment.
Frequently Asked Questions
What is SOC-as-a-Service?
SOC-as-a-Service gives your business a fully staffed security operations center as a subscription. Our team of analysts monitors your organization’s environment 24/7, investigates threats, and responds, without requiring your business to hire, train, or house a security team.What is the difference between co-managed and fully managed SOC?
A co-managed SOC wraps the security tools you already own and works alongside your internal IT team. A fully managed SOC means we deploy and run the entire stack and own detection and response end to end. The right choice depends on how much internal IT capacity you have.Will a managed SOC replace my IT team?
No. It extends their capabilities. Your IT team keeps running your business technology while our SOC handles round-the-clock security monitoring and response, the hardest and most expensive aspect to internal staff.How fast can a managed SOC be up and running?
Most environments are onboarded in a matter of days. Our team connects to your existing tools, tunes detections to your environment, and begins monitoring, with full coverage typically live within the first week or two.