
Find out what MDR would catch in your environment. Start with a free exposure assessment
Key Points
- MDR pairs AI-driven detection with human analysts who investigate and respond.
- Coverage spans six signal domains, not just endpoints.
- Confirmed threats are contained in minutes, not queued as tickets.
- A managed service, so there is nothing for your team to run or tune.
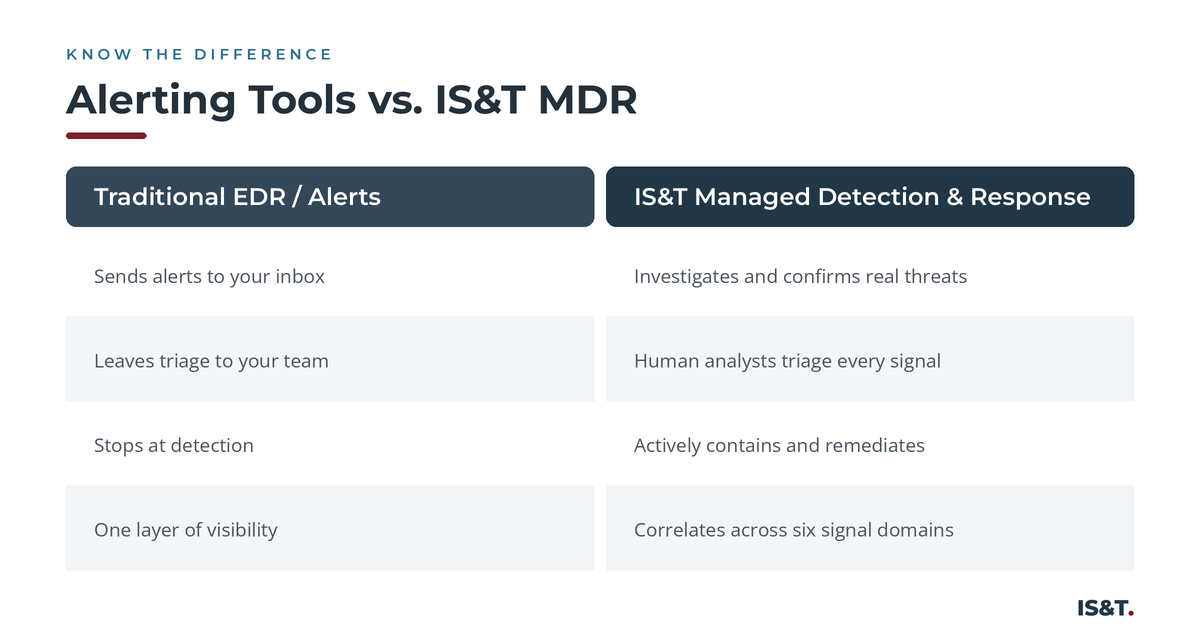
Managed detection and response, or MDR, is a service that finds threats across your business environment, confirms which are real, and responds to stop them. The last part is what sets MDR apart. Traditional tools simply detect and alert, leaving the hard work of triage and response to you. IS&T's MDR closes that loop with experienced human analysts who investigate every signal and take direct containment action so a detected threat becomes a contained one as fast as possible.
Alerts do not stop attacks. Response does.
An alert is only useful if someone acts on it quickly and correctly. Most security tools flood teams with alerts, many of which are false positives, allowing the real one to get overlooked. MDR fixes that problem by putting expert analysts on your alerts around the clock and empowering them to respond.
What happens the moment something looks wrong
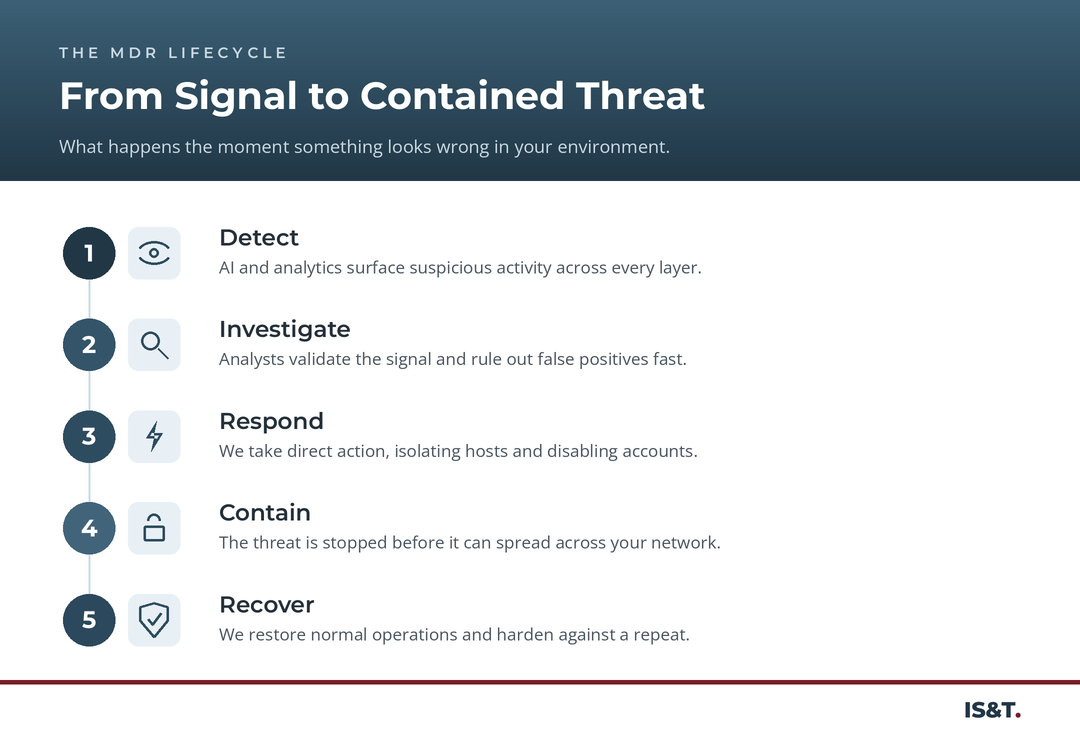
When your business is protected by MDR, there is a defined process that kicks in when a concerning signal appears. Our team detects, investigates to rule out noise, responds by taking direct action, contains the threat so it cannot spread, and then recovers the system. The whole cycle is designed to move at the speed of the attack.
Coverage across every signal domain
Modern attacks move quickly. A stolen credential becomes a cloud misconfiguration becomes data exfiltration. MDR that only watches endpoints misses that journey. We correlate across endpoint, identity, network, cloud, application, and data. We see the full attack, not just one frame of it.
Beyond EDR and XDR
EDR and XDR are valuable tools, but they still require people to run them, tune them, and respond to what they find. MDR is the managed service that makes those tools actually protect your business, adding the human expertise and 24/7 response that software alone cannot provide.
Want to see what is slipping past your current tools? Book a conversation and we will show you how MDR would cover the gaps.
Frequently Asked Questions
What is managed detection and response (MDR)?
MDR is a security service that combines technology and human analysts to detect threats across your business environment, investigate them, and respond, including taking action to contain them. It goes beyond alerting by actually stopping confirmed threats.How is MDR different from EDR?
EDR (endpoint detection and response) is a tool that watches endpoints and generates alerts. MDR is a service that watches EDR and the entire system. MDR has real analysts investigate and respond. While EDR gives you data, MDR gives you outcomes.Does MDR only cover endpoints?
No. Strong MDR correlates signals across six domains: endpoint, identity, network, cloud, application, and data. Attacks rarely stay in one place, so watching only endpoints leaves gaps.What happens when MDR finds a real threat?
Our analysts validate the threat and respond directly. The process includes isolating affected hosts, disabling compromised accounts, and removing the attacker's foothold. All of this occurs within minutes and is followed by the recovering and hardening of the environment.