
Talk through your goals with a security leader. Book a no-cost vCISO consultation.
Key Points
- A vCISO gives your business a seasoned security executive on a fractional basis.
- Deliverables include risk assessment, roadmap, policy, and board reporting.
- The fastest path to SOC 2, HIPAA, PCI DSS, and other compliance goals.
- Strategic leadership that pairs with our SOC and MDR for execution.
A virtual CISO, or vCISO, is an experienced security executive who leads your security program without being a full-time hire. For most growing businesses, a full-time chief information security officer is cost prohibitive. Yet the need for security leadership is real, especially when a big customer, an auditor, or an incident forces the issue. IS&T's vCISO service gives your organization that leadership on demand: someone to set the strategy, build the plan, and own the outcomes.
What your vCISO delivers
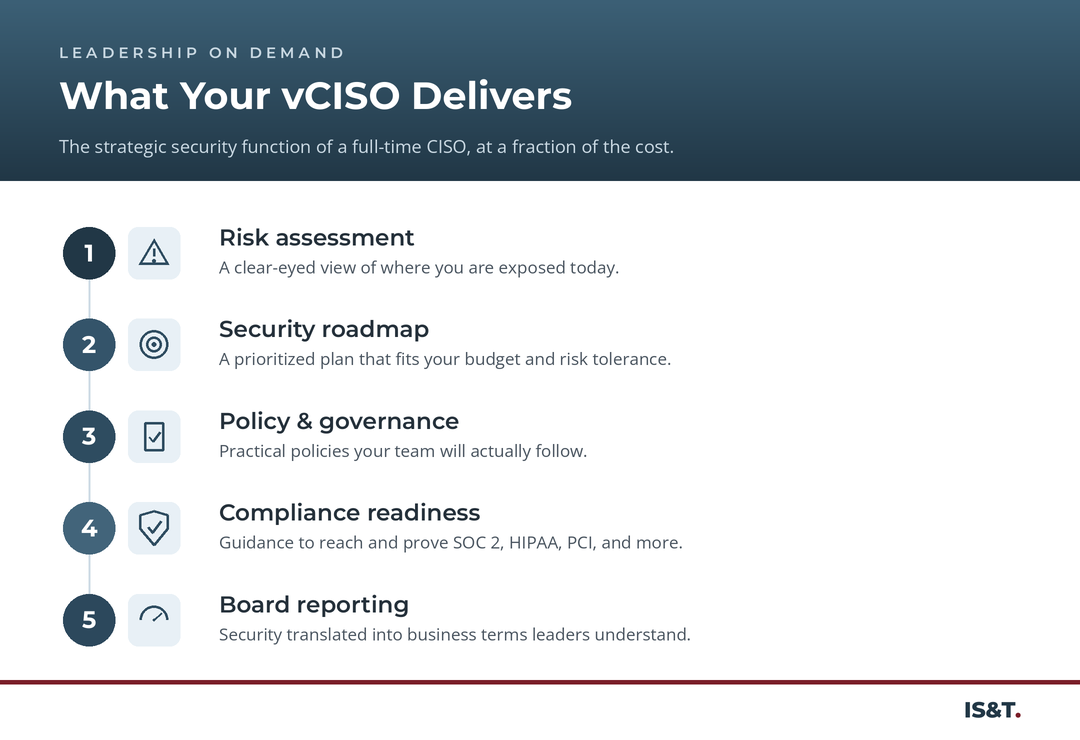
A vCISO is not simply an advisor who hands your business a report and leaves. They take ownership of your organization’s security direction, from understanding where you need support to building and driving the plan that closes those gaps, in language your in-house leadership and board can act on.
The fast path to compliance
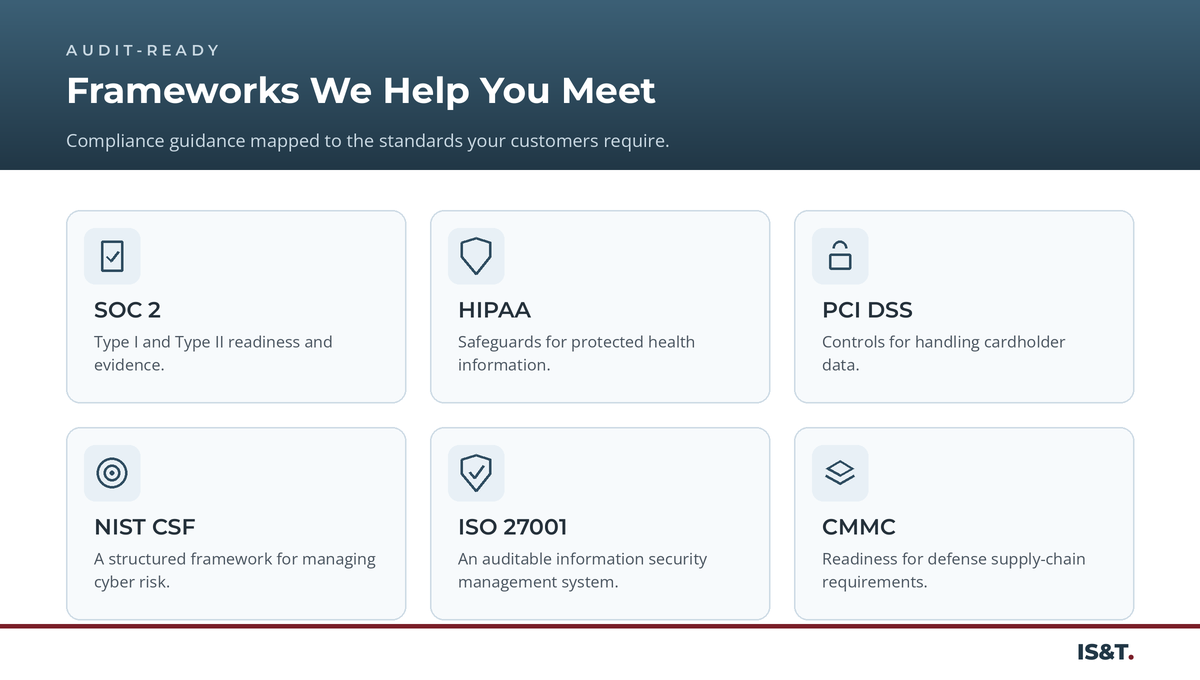
Most vCISO engagements are driven by a compliance need. Whether a customer requires SOC 2, your business is entering healthcare under HIPAA, or your organization handles card data under PCI DSS, a vCISO knows exactly what auditors look for and gets your team there efficiently, without wasted effort or false starts.
Strategy that connects to execution
Security strategy is only worth something if it gets executed correctly. Because IS&T also runs the SOC, MDR, and SIEM services that carry out the plan, your vCISO is never writing recommendations into a vacuum. The roadmap built is one we can actually operate, end to end.
Board-ready reporting
Your organization’s leadership does not want raw security metrics, they want to understand risk in business terms. A vCISO translates your security posture into clear reporting that supports budget decisions and satisfies boards, investors, and customers asking hard questions about how their data is protected.
Bring your security goals and questions. A short vCISO consultation will show you the fastest path forward, at no cost.
Frequently Asked Questions
What is a virtual CISO (vCISO)?
A virtual CISO is an experienced security executive who leads your security program on a part-time or fractional basis. You get the strategy, governance, and board-level guidance of a chief information security officer without the cost of a full-time hire.When does a business need a vCISO?
Common triggers are a customer or contract requiring SOC 2 or similar, a recent security incident, entering a regulated market, or simply growing past the point where security can stay informal. A vCISO brings order and a plan.What does a vCISO actually do?
vCISO assesses your current risk, builds a prioritized security roadmap, establishes policies and governance, guides compliance efforts, and translates security into business terms for your leadership and board.How is a vCISO different from a managed SOC
A managed SOC is the operational team that monitors and responds to threats. A vCISO is the strategic leadership that decides what your security program should be. They complement each other: strategy on top, operations underneath.