
Get a managed SIEM quote scoped to your environment and log volume.
Key Points
- We run the full SIEM lifecycle: collection, correlation, tuning, and analyst review.
- Continuous tuning turns alert noise into signal you can trust.
- Available fully managed or co-managed alongside your internal team.
- Audit-ready logging and reporting for SOC 2, HIPAA, and PCI DSS.
A SIEM, or security information and event management platform, is the system that collects logs from across your environment and correlates them to surface threats. It is powerful and, for many frameworks, required, but it is notoriously demanding to run well. Managed SIEM hands that work to our team. IS&T collects your logs, writes and continuously tunes the detection rules, and puts analysts on the output 24/7, so you get the value of a SIEM without hiring and retaining SIEM engineers.
Why SIEMs fail without the right team
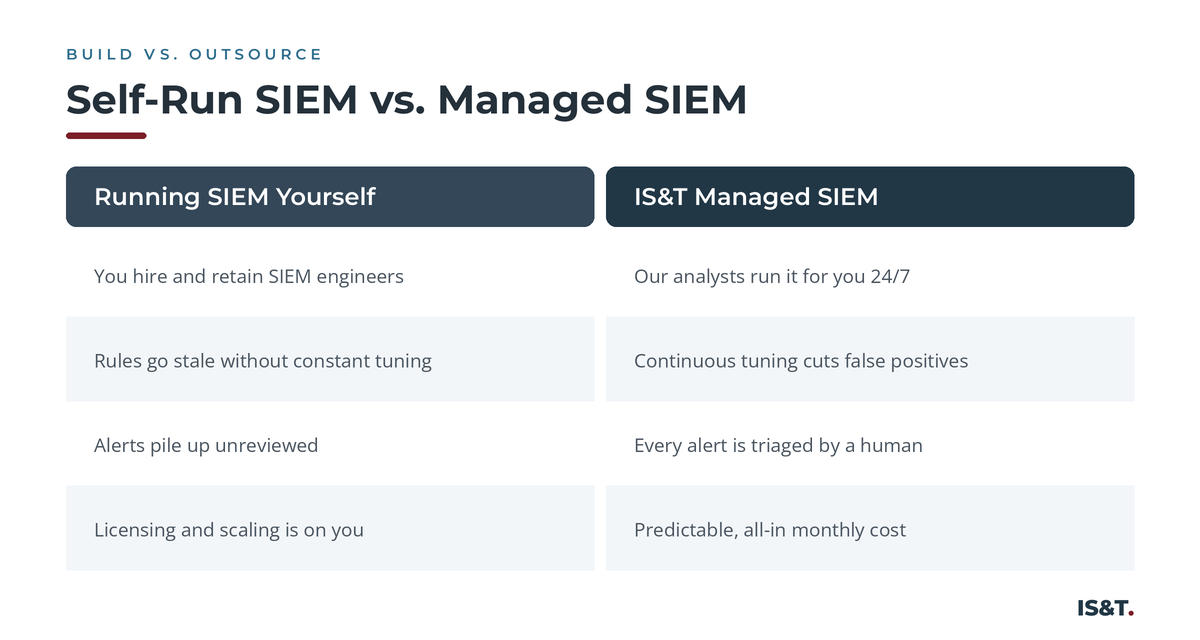
Most SIEM disappointments are not tool problems, they are staffing problems. Rules go stale, alerts pile up unreviewed, and the platform becomes an expensive backlog. A SIEM only protects your business if someone is constantly overseeing and investigating what they find. That is exactly what we provide.
What our managed SIEM includes
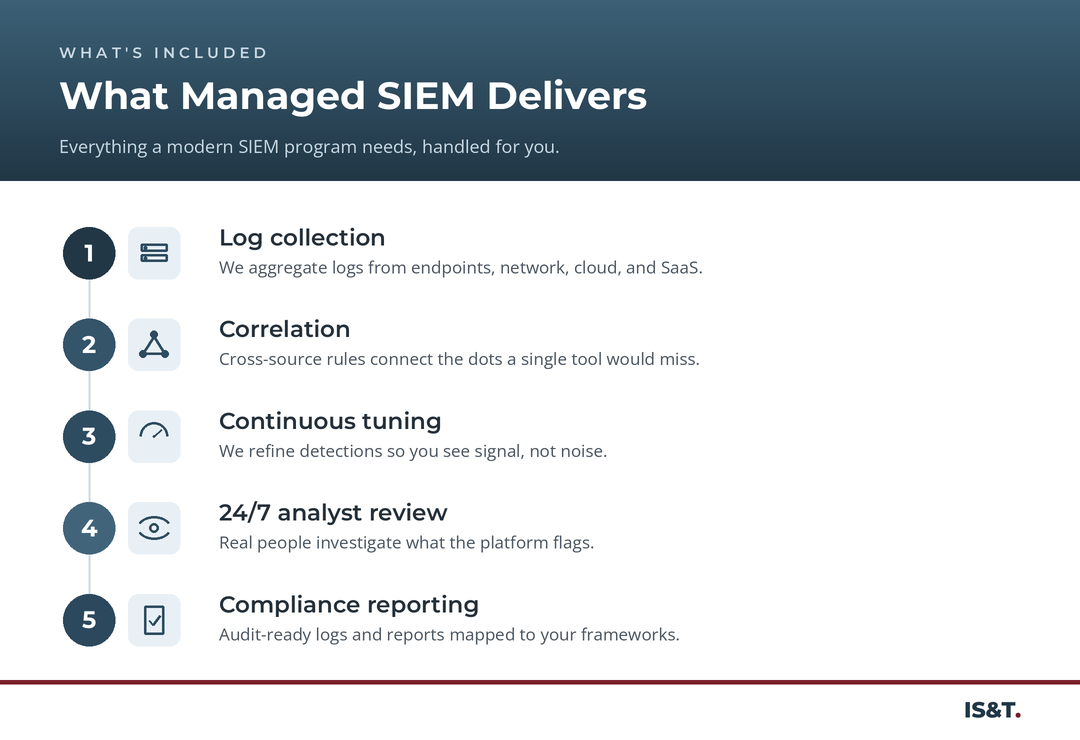
We handle the entire lifecycle so nothing falls through the cracks: aggregating logs from every source, correlating them with cross-source rules, tuning to cut false positives, reviewing alerts with human analysts, and producing the reports your auditors want.
Fully managed or co-managed
If you have already invested in a SIEM but cannot staff it 24/7, co-managed SIEM lets our team run it alongside your in-house staff while your business keeps visibility and control. If your organization is starting fresh, fully managed SIEM means our team handles everything end to end. Either way, your business gets around-the-clock coverage.
Built for compliance
Centralized logging and retention are non-negotiable for most compliance frameworks. Managed SIEM gives your business the tamper-resistant records, retention windows, and reporting that SOC 2, HIPAA, PCI DSS, and similar standards require, and pairs naturally with our virtual CISO service for the broader program.
Tell us about your environment and log sources, and we will scope a managed SIEM plan and quote for you.
Frequently Asked Questions
What is managed SIEM?
Managed SIEM is a service where a provider runs your business’s security information and event management platform by collecting logs, writing and tuning correlation rules, and having analysts review what it flags, 24/7. Your organization gets the SIEM outcome without hiring SIEM engineers.What is the difference between managed and co-managed SIEM?
With managed SIEM, our team runs the platform entirely. With co-managed SIEM, we operate it alongside your internal team, who keep visibility and some control. Co-managed suits organizations that own a SIEM but cannot staff it around the clock.Do I need a SIEM if I already have MDR?
They serve different purposes. SIEM centralizes and correlates logs across your organization’s whole environment and is often required for compliance. MDR focuses on detection and response. Many organizations use both, and our managed SIEM feeds our detection and response service.Will managed SIEM help with compliance?
Yes. Centralized logging, retention, and reporting are core requirements of frameworks like SOC 2, HIPAA, and PCI DSS. Managed SIEM produces the audit-ready records and reports those frameworks expect.